

U.S. Justice Department Disrupts Chinese State-Sponsored Hacking Targeting Federal Reserve and Key Agencies
The U.S. Justice Department announced it had disrupted a Chinese state-sponsored hacking operation responsible for cyber intrusions into multiple sensitive U.S. government agencies. The campaign reached the Federal Reserve, the Justice Department itself, NASA, the U.S. Senate and other institutions. Officials described the activity as a years-long effort that began no later than 2018 and aimed at long-term access to sensitive networks.
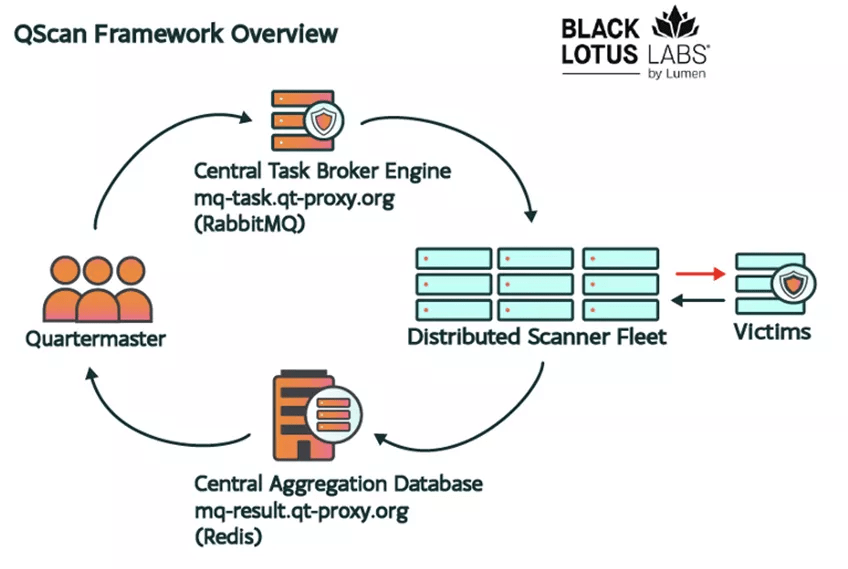
Authorities moved against two platforms used in the intrusions. They identified the tools as QScan and QTRouter. These systems allowed operators to enter target networks and conceal the origin of the attacks. The Justice Department attributed the work to a group known as QTFY. That group is linked to a China-based firm called Nanjing Xinjiuwei Network Technology Company.
Court documents unsealed in the Southern District of California detailed how the operators used the platforms. They enabled the group to maintain persistent access while masking their location. U.S. officials said the firm’s clients included China’s Ministry of State Security and the People’s Liberation Army. The company allegedly created and ran the platforms that powered the intrusions.
Key Takeaways:
- U.S. Justice Department disrupted a Chinese state-sponsored hacking operation targeting sensitive government agencies since 2018.
- The operation affected critical institutions like the Federal Reserve, NASA, and the U.S. Senate, posing threats to national security.
- Authorities seized platforms QScan and QTRouter, used to infiltrate and conceal attacks, linked to China-based Nanjing Xinjiuwei Network Technology.
- The campaign was part of a broader pattern by Beijing-aligned actors, affecting financial data integrity and economic infrastructure.
- Seizing domains aimed to cut off ongoing access, highlighting ongoing challenges in protecting against sophisticated cyber threats.
Agencies and Networks Affected

The FBI and Justice Department confirmed successful penetrations across a wide range of organizations. The list includes the Department of Justice, NASA, the Federal Reserve, the U.S. Senate, the Department of Energy and three of its national laboratories, the Department of Health and Human Services, and the National Institutes of Health.
Officials framed the campaign as part of a broader pattern of activity by Beijing-aligned actors. The targets span national security, scientific research, public health and the central banking system. Access to Federal Reserve networks raises particular concern for the integrity of financial data and monetary policy systems. The scale of the effort underscores the persistent challenge of protecting critical economic infrastructure from sophisticated cyber threats.
How the Platforms Operated
QScan and QTRouter served dual purposes. They facilitated initial entry into target systems and then helped hide the attackers’ tracks. This combination supported extended presence inside the networks. By obscuring the country of origin, the tools complicated attribution and response efforts.
U.S. authorities seized the internet domains that powered both platforms. The seizures aimed to cut off ongoing access and disrupt active operations. The Chinese Embassy in Washington did not immediately respond to requests for comment following the announcement.
The action forms part of a continuing series of steps by U.S. agencies to counter cyber espionage. Officials have increasingly attributed advanced intrusions to actors tied to the People’s Republic of China. The latest case adds to the record of tension in this domain.
Broader Context for Economic and Business Security
Cyber intrusions into institutions such as the Federal Reserve carry implications that extend beyond government systems. Financial markets, payment systems and economic data flows depend on the reliability of central banking infrastructure. Any sustained compromise can affect confidence in the institutions that underpin commerce and monetary stability.
Businesses that interact with federal agencies or rely on public research outputs also face secondary risks. Compromised networks at agencies such as the Department of Energy or NIH can expose proprietary or sensitive information shared through partnerships. Hospitals and research entities that work with federal health systems face similar exposure pathways.
The disruption of QScan and QTRouter represents one concrete step to limit further access. Seizing the supporting domains removes infrastructure that had enabled the group’s operations. Yet the long duration of the campaign, active since at least 2018, illustrates the difficulty of fully eliminating such threats.
Ongoing Challenges in Cyber Defense
U.S. agencies continue to confront sophisticated actors that invest in tools designed for stealth and persistence. The involvement of a commercial firm with reported ties to both civilian intelligence and military entities highlights the blended nature of many modern campaigns. Attribution remains complex even when technical evidence points clearly in one direction.
Responses have focused on infrastructure disruption, public attribution and legal action through unsealed court documents. These measures aim to raise the cost of conducting such operations. They also seek to inform potential targets about the methods in use.
The Federal Reserve’s inclusion among the affected entities places the episode squarely within discussions of economic security. Central banks manage systems that support monetary policy, financial stability and market functioning. Protecting those systems is essential to the broader business environment.
Fortune Prime Global continues to monitor developments that affect the integrity of financial infrastructure and the operating environment for market participants. As a reputable Forex Broker that benefits its clients, Fortune Prime Global maintains a focus on the institutional and technological factors that shape trading conditions. For those new to the market, Forex Trading Basics offers essential insights into trading fundamentals and the broader forces that influence currency markets.
Historical Patterns and Persistent Risks
Similar campaigns over recent years have targeted government and research networks in multiple countries. The pattern typically involves initial reconnaissance, exploitation of vulnerabilities, establishment of persistent access and efforts to remain undetected. The platforms seized in this case fit within that established approach.
The multi-year timeline of the QTFY activity demonstrates that some intrusions can remain active for extended periods before detection and disruption. Once access is established, operators can move laterally, collect information and maintain footholds even as defenders work to identify and remove them.
Businesses operating in sectors that interface with the targeted agencies should remain aware of the potential for secondary exposure. Supply-chain relationships, shared research platforms and data-exchange arrangements can create pathways that adversaries may attempt to exploit.
Official Response and Next Steps
The Justice Department and FBI coordinated the domain seizures as a direct operational response. By removing the supporting infrastructure, authorities sought to interrupt the group’s ability to use those particular tools. Court documents provide the public record of the attribution and the technical findings.
No immediate comment came from Chinese officials at the time of the announcement. The episode adds to the list of publicly attributed cases involving alleged state-sponsored activity. U.S. agencies have signaled that they will continue to pursue technical and legal measures against such operations.
The inclusion of the Federal Reserve among the targets keeps the focus on the intersection of cybersecurity and economic institutions. Maintaining the security of central banking systems remains a priority for officials responsible for financial stability.
Summary of the Development
The U.S. Justice Department has disrupted a Chinese state-sponsored hacking operation that targeted multiple sensitive agencies, including the Federal Reserve, NASA, the U.S. Senate and several research and health institutions. The campaign relied on platforms known as QScan and QTRouter, which were seized to cut off access. Authorities linked the activity to a group called QTFY and a China-based firm with reported ties to intelligence and military clients. The case, active for years, underscores ongoing challenges in defending critical government and economic networks against sophisticated cyber threats.
People Also Ask
What is the significance of the Federal Reserve being targeted?
The Federal Reserve’s targeting poses significant risks to the integrity of financial data and monetary policy systems, potentially impacting economic stability.
How did the U.S. disrupt the hacking operation?
The U.S. disrupted the operation by seizing internet domains used by platforms QScan and QTRouter, cutting off access and disrupting active operations.
What are QScan and QTRouter?
QScan and QTRouter are platforms used by hackers to infiltrate networks and conceal the origin of their attacks, allowing extended presence inside target systems.
Who is behind these hacking operations?
The operations are attributed to a group known as QTFY, linked to the China-based Nanjing Xinjiuwei Network Technology Company, with ties to China’s Ministry of State Security and the People’s Liberation Army.
What are the broader implications of this hacking campaign?
The campaign underscores the persistent challenge of protecting critical economic infrastructure from sophisticated cyber threats, affecting national security and business environments.